AWS WAF
Overview
This section rebuilds the recommendations from the AWS WAF Best Practices guide in NSM, including the AWS Managed Rules and the Recommended WAF Rule Order. We recommend this build as a best practice for managing AWS WAF with NSM.
The exact code for this build is in the accompanying GitHub repository. This section reviews each part of the build and explains what it outputs and why it's included.
Rule sections and NSM policy priority
A web ACL that NSM manages evaluates WAF rules in three sections, from top to bottom in the following table. Together, the three sections are the complete WAF rule order.
| Runs | Section | Who manages it | Can a local operator override it? |
|---|---|---|---|
| First ⬇ | Pre-process rule groups | NSM | No |
| Next ⬇ | Local web ACL rules | The account's operator, such as an application team | Not applicable |
| Last | Post-process rule groups | NSM | Yes. Local web ACL rules run first. |
The difference between the two centrally managed sections, pre-process and post-process rule groups, is who gets the last word. NSM rules in pre-process rule groups run before any local web ACL rule, so a local operator can't override them. NSM rules in post-process rule groups run after the pre-process rule groups and after the local web ACL rules, so a local operator can act on a request before they run. For example, a local Allow rule ends evaluation before the post-process rule groups see the request.
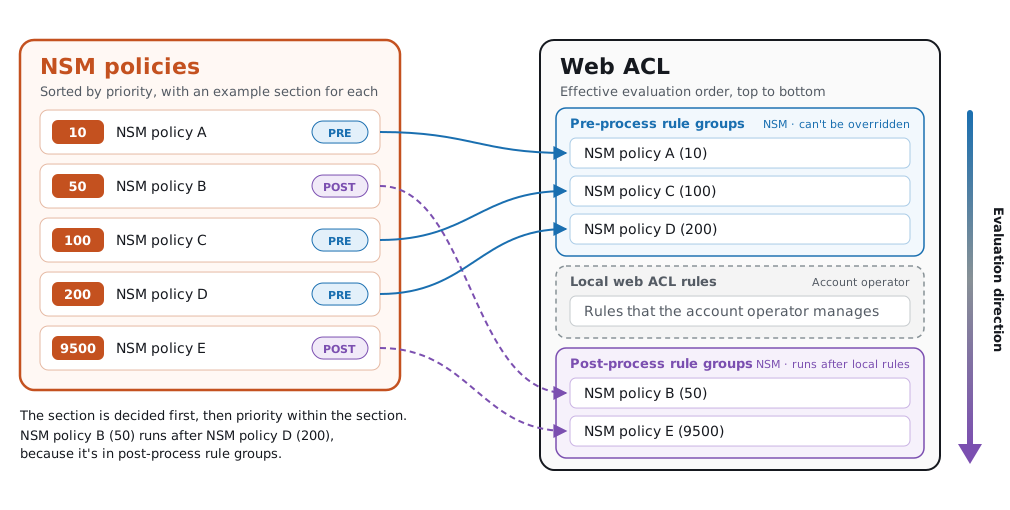
NSM policy priority doesn't move an NSM rule between sections. The section decides where an NSM rule runs in the web ACL, and priority decides the order of NSM rules within that section. For example, an NSM policy at priority 50 in post-process rule groups runs after an NSM policy at priority 9500 in pre-process rule groups, because every pre-process rule group runs before every post-process rule group.
The following example shows five NSM policies, each assigned to pre-process or post-process rule groups, and the order that the web ACL evaluates them in.
Labels affect which section to use. WAF rules in post-process rule groups can read labels that pre-process rule groups add, but not labels that local web ACL rules add. A local operator who wants to grant an exception to an NSM rule in post-process rule groups therefore uses a local Allow rule, not an exception label. For more information, see Creating Exceptions in the AWS WAF Best Practices guide.
AWS WAF sections
- Recommended Design – The recommended AWS WAF NSM policies in priority order
- Rule Examples – The configuration of each NSM rule in those NSM policies
- Label-Based Exceptions – Grant application exceptions to AMRs at scale